Topic
#Reverse
9 articles
Hack Yourself: Reversing the Program That Came Without a Manual
An interactive essay on reading the world, and myself, the way I read a malware sample: a program with no manual, a malware report on that program with six findings (Fun included), a triage window, a trace log, a breakpoint and a git history. The skills I thought were obsolete still transfer, once I learn to export them.
Read essay
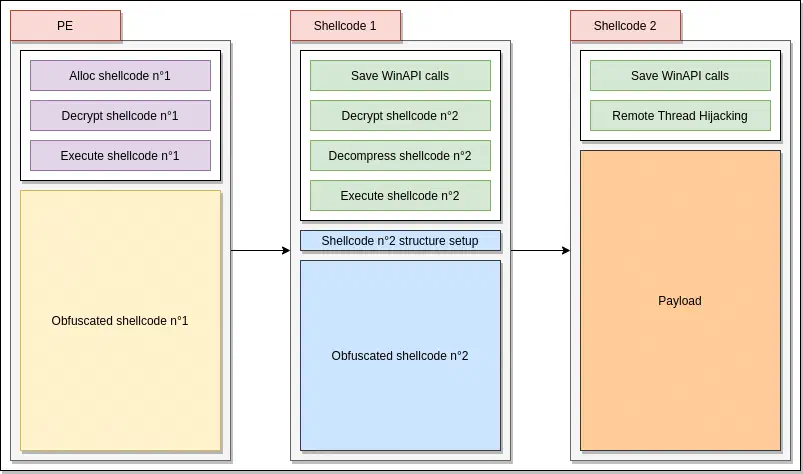
Anatomy of a simple and popular packer
A walkthrough of a simple, widely used packer: its architecture, the PE stub and the shellcode stages that unpack the final payload.
Read teardown
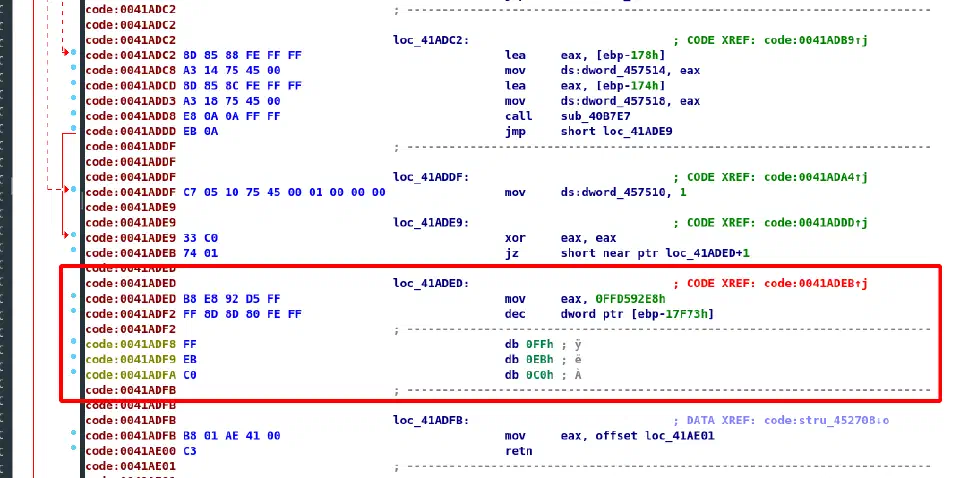
Let's play (again) with Predator the thief
A second look at Predator the Thief, focused on how a newer version of the stealer was built and what changed in its code.
Read teardown
Haruko Malware Tracker - 1 Year Anniversary Update
An update one year after launching Haruko, my solo malware tracker, and what it offers for OSINT work and learning malware analysis.
Read teardown
Overview of Proton Bot, another loader in the wild!
An overview of Proton Bot, a malware loader seen in the wild in 2019: how it works and what it can do.
Read teardown
Let's nuke Megumin Trojan
A reverse-engineering walkthrough of Megumin Trojan, a C++ malware sold on underground forums, and of what it can do.
Read teardown
Let's play with Qulab, an exotic malware developed in AutoIT
Qulab, a password stealer and clipper written in AutoIt: how its code is obfuscated and executed, its features and its Telegram bot C2.
Read teardown
Let's dig into Vidar - An Arkei Copycat/Forked Stealer (In-depth analysis)
An in-depth analysis of Vidar, an info-stealer forked from Arkei, and of how it differs from the malware it copies.
Read teardown
Predator The Thief: In-depth analysis (v2.3.5)
An in-depth analysis of Predator the Thief v2.3.5, an info-stealer written in C/C++, from its hidden C2 to the data it steals.
Read teardown
No articles match that filter.