Year in review
2019
6 articles published in 2019. See every year →
Let's play (again) with Predator the thief
A second look at Predator the Thief, focused on how a newer version of the stealer was built and what changed in its code.
Read teardown
Haruko Malware Tracker - 1 Year Anniversary Update
An update one year after launching Haruko, my solo malware tracker, and what it offers for OSINT work and learning malware analysis.
Read teardown
Overview of Proton Bot, another loader in the wild!
An overview of Proton Bot, a malware loader seen in the wild in 2019: how it works and what it can do.
Read teardown
Let's nuke Megumin Trojan
A reverse-engineering walkthrough of Megumin Trojan, a C++ malware sold on underground forums, and of what it can do.
Read teardown
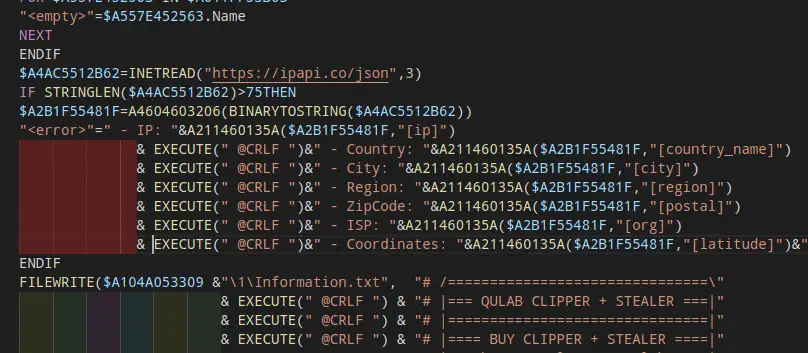
Let's play with Qulab, an exotic malware developed in AutoIT
Qulab, a password stealer and clipper written in AutoIt: how its code is obfuscated and executed, its features and its Telegram bot C2.
Read teardown
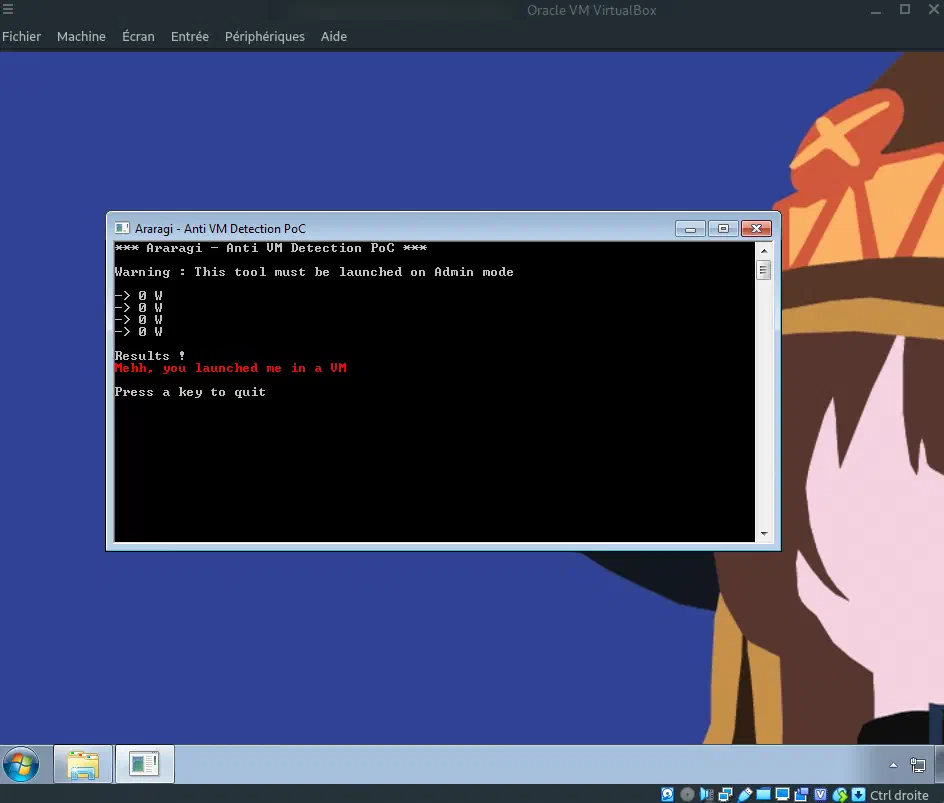
CPU Power Usage - Sandbox Evasive Technique
A short proof of concept for detecting a virtual machine or sandbox by looking at CPU power usage.
Read teardown